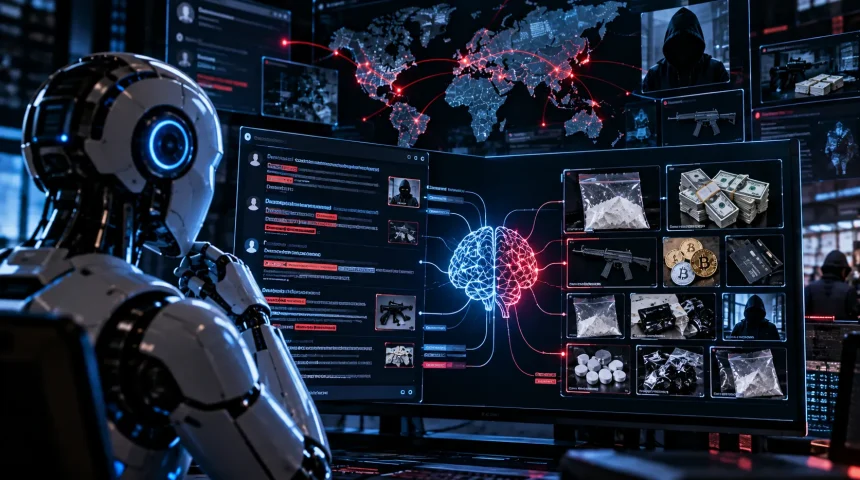
Researchers at G.H. Raisoni University published a study in Neural Computing and Applications this week describing a multimodal AI framework for dark web threat detection. The system uses a hybrid CNN-RNN architecture combined with a Multi-Modal Semantic-Attention Fusion (MSAF) mechanism to classify dark web forum content by analyzing text, images, and behavioral signals together in real time. The authors argue it achieves substantially higher accuracy than single-modality approaches, and represents a significant step forward in automating what human analysts currently do manually.
Drug marketplaces run on product photographs. Weapons trafficking relies on proof images. Ransomware groups post screenshots of victim systems. Data brokers upload image files alongside credential dumps. Increasingly, criminals use images to hide information in plain sight through steganography, encoding data inside image files in ways that bypass text-based scanning entirely.
A research paper published this week in Springer’s Neural Computing and Applications addresses that gap directly. Researchers Yogita H. Dhande and Amol V. Zade at G.H. Raisoni University in Amravati, India have built an AI framework that reads dark web forum content across text and images simultaneously, fusing both into a single classification pipeline that, the authors argue, outperforms any text-only or image-only approach on this problem.
Why Text-Only Tools Have Been Insufficient
Every existing dark web intelligence platform, including the text-based tools powering services like KELA’s criminal forum monitoring in the Fujitsu partnership, builds its detection on one data type: scraped text from forum posts and marketplace listings.
That approach works reasonably well for explicit text content. A threat actor who types “selling 100,000 credit card records” in a forum post gets flagged. But it fails in three specific scenarios that have grown more common as criminal communities have adapted to monitoring pressure.
First, image-based communication: product photos, document scans, screenshot-based proof of access or data theft. These convey information that text scrapers cannot see. A ransomware group that posts a screenshot of a victim’s file directory to prove access never types those filenames into text.
Second, steganography: hiding data inside image files themselves. A forum post with an attached image that appears to be a product photo may contain encrypted communication, exfiltration data, or hidden URLs in its pixel values. No amount of text analysis catches this.
Third, context collapse: forum posts where the meaning depends on cross-referencing a text claim with an attached image. “Same product, same quality” means nothing without seeing what product the image shows.
The 2026 CMES survey of AI-based threat detection for illicit web ecosystems reaches the same conclusion: that text-only detection “may be insufficient for resilient zero-day defense” and that multimodal integration is the necessary direction.
What the Research Actually Built
The Dhande and Zade system has three core technical components working together.
The CNN-RNN hybrid architecture fuses image and text analysis. Convolutional Neural Networks (CNNs) were originally developed for image recognition. They identify patterns in visual data by looking at local features and how they combine. Recurrent Neural Networks (RNNs) handle sequential data like text, processing words in order and maintaining context across a sentence or paragraph. Combining both into a single architecture lets the system extract visual features from an image and semantic meaning from the accompanying text, without treating them as two separate analytical problems.
The Multimodal Semantic-Attention Fusion (MSAF) mechanism makes the combined analysis coherent. The challenge with multimodal AI isn’t just processing text and images separately. It’s linking them so each informs the other’s interpretation. MSAF maintains what the researchers call “semantic consistency” between modalities: if a forum post discusses pharmaceutical packaging and an attached image shows pills, those two signals reinforce each other rather than being processed in isolation. This is how a human analyst actually reads dark web forum content.
Transfer learning lets the system adapt to the domain-specific language and visual content of the dark web without training from scratch on a massive dark web dataset. Instead, it starts with a pre-trained foundation. It fine-tunes on dark web-specific material, enabling it to understand criminal community vocabulary, product categories, and visual conventions without the researcher having to build a billion-record training corpus.
Behavioral modeling is the fourth layer, and the most novel. Rather than looking only at content, the system also analyzes activity patterns: post frequency, account interaction histories, timing, and network relationships between actors. A new account that posts 47 times in an hour and uses references to known threat actor terminology triggers a different classification than an established community member asking about operational security.
How This Differs from DarkBERT
The most relevant comparison is DarkBERT, the dark web intelligence model developed by S2W and KAIST in 2023, which trained a language model specifically on millions of dark web pages and achieved 90% accuracy in classifying illegal activities.
DarkBERT was a significant step because it was trained on actual dark web content rather than generic text. But it’s still a text model. It understands criminal vocabulary, dark web-specific terminology, and forum language patterns better than a general-purpose LLM. It cannot see images.
Dhande and Zade’s framework complements rather than replaces that approach. The text understanding component of their architecture could in principle be seeded with a DarkBERT-style language representation. The image analysis and behavioral modeling layers add dimensions that DarkBERT doesn’t have.
The practical implication: a system built on this architecture would flag threats that DarkBERT misses, because it can see the product photographs, screenshot evidence, and steganographic content that text-only monitoring leaves dark.
Why This Research Arrives at the Right Moment
The timing matters. The dark web intelligence market is growing at over 21% annually; CRIF’s H1 2026 data showed 2.5 billion records circulating in criminal markets in six months. The CRIF Cyber Observatory report showed criminal communities are producing increasingly image-heavy content alongside text, particularly in financial fraud listings.
At the same time, the adversarial AI picture has shifted. Anthropic’s September threat intelligence report documented how criminal actors are already using AI to make fraud more sophisticated. Cybersecurity researchers are racing to build the detection equivalent: AI that keeps pace with AI-generated criminal content, including AI-generated images used to test and probe financial fraud systems.
A multimodal threat detection framework that understands both text and images is inherently more resistant to AI-generated content evasion than a text-only system. You can generate convincing text with an LLM. Generating an image that evades both a text classifier and a CNN-based image classifier simultaneously requires substantially more effort.
The Gap Between Research and Deployment
The honest caveat with this kind of research paper is the distance between a validated academic framework and a production-ready threat intelligence tool. The Dhande and Zade paper reports results on controlled datasets. Real-world dark web monitoring involves continuously shifting content, new criminal community conventions, and adversarial actors who specifically try to evade detection tools.
Commercializing this kind of research typically takes 18 to 36 months. The commercial dark web intelligence platforms, the ones powering services like Nasdaq Verafin’s fraud intelligence partnership, will be watching this closely. The multimodal gap is real and recognized. The academic proof of concept is now published. The gap between the two is where the next generation of commercial dark web intelligence tools will be built.
Frequently Asked Questions
What did the researchers build?
A multimodal AI framework that reads dark web forum content across text, images, and behavioral signals simultaneously using a hybrid CNN-RNN architecture and a Multimodal Semantic-Attention Fusion (MSAF) mechanism.
Why does this matter if text-based tools already exist?
Text-only tools miss image-based communications, steganographic content, and context that emerges only when you read text and images together, the same way a human analyst does.
How is this different from DarkBERT?
DarkBERT is a text-only model trained on dark web pages. The new framework adds visual analysis and behavioral modeling. The two approaches complement each other rather than compete.
Where was this published?
Neural Computing and Applications, a peer-reviewed journal from Springer, by Yogita H. Dhande and Amol V. Zade of G.H. Raisoni University, Amravati, India.
Is this available as a product?
Not yet. It’s an academic framework. Commercial dark web intelligence platforms will likely incorporate these techniques over the next one to three years.