Google’s Threat Intelligence Group has warned of a surge in two related AI-access attacks: credential theft targeting AI service accounts (resold at up to a 97% discount on dark web markets), and server-compromise attacks where hackers deploy AI workloads on breached enterprise cloud systems, shifting the compute cost onto victims. Anthropic independently confirmed that threat actors in more than 24 countries were exploiting its Claude tools for malicious purposes. Hultquist warned that “every threat actor is using AI.
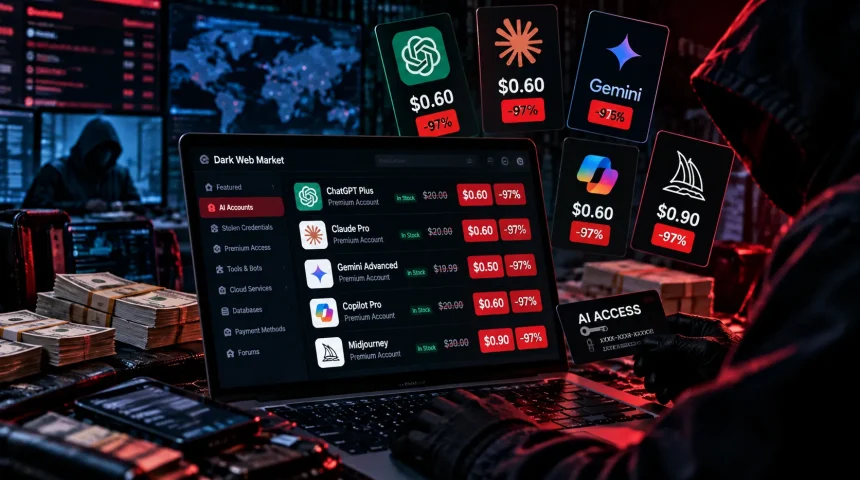
John Hultquist, chief analyst at Google’s Threat Intelligence Group, told the Financial Times on September 28, 2026, that his team is observing a sharp rise in what the security industry now calls LLM-jacking, a category of attack targeting access to AI models rather than traditional corporate data. The market has become organized enough that dark web vendors compete on price, offering unauthorized access to premium AI services at discounts up to 97% and building customer service infrastructure to keep buyers supplied.
What LLM-Jacking Actually Is
Sysdig’s threat research team coined the term when they first documented the attack pattern in 2024. At the time, it was a niche concern: a few actors using stolen cloud credentials to access AI APIs quietly. Two years later, Google’s GTIG is describing it as a “burgeoning economy.”
The attack comes in two distinct forms, and understanding the difference matters for what businesses need to defend against.
The first model is credential theft and resale.
Criminals steal usernames and passwords for AI service accounts, the same type of credential theft that feeds every other underground market, and sell them on dark web forums at deep discounts. A subscription to Claude or ChatGPT that costs $200 a month can sell for a handful of dollars on these markets, or sometimes less. The buyer gets AI access without paying the provider. The seller profits from data that often costs them nothing after the initial credential harvest from a breach or infostealer run.
What’s new in 2026, and what signals market maturity, is the replacement guarantee service. Some vendors now promise that if an account is suspended or revoked, they’ll provide a replacement credential at no additional charge. This mirrors the “validity guarantees” that carding shops have offered on stolen payment cards for years, as we covered in our breakdown of how threat actors vet dark web carding shops. The same criminal market logic applies: buyers need confidence they’re getting working product, and sellers who can guarantee replacements command higher trust ratings and better business.
The second model is server compromise for compute.
Instead of stealing someone else’s AI account, attackers breach an enterprise cloud environment and deploy their own AI models directly on the victim’s infrastructure. Every AI query the attacker runs generates compute costs billed to the victim. Hultquist described this as mirroring earlier cryptojacking operations, where hackers hijacked machines to mine cryptocurrency on the victim’s electricity bill. Same principle, much more expensive: AI inference at scale can cost thousands of dollars per day in cloud compute charges.
Why AI Access Became a Dark Web Commodity
The simple reason is price. Premium AI subscriptions are expensive relative to what a single stolen account costs to obtain. When bulk credential harvesting from breaches and infostealer malware can generate thousands of accounts for negligible cost per unit, and the resale market for each account is $5 to $10, the economics work easily.
The CRIF Cyber Observatory found 2.5 billion records circulating on the dark web in H1 2026 alone, with credentials being the single most common data type. Email and password combinations, the exact pairing that unlocks AI service accounts, appeared together in 95.9% of examined records. A significant fraction of those email addresses belong to people who have also signed up for AI services, simply because AI services are now mainstream consumer and enterprise products.
Credentials acquired from breaches like the Substack incident, where 663,000 email and password combinations entered circulation, feed into this pipeline. Anyone who used the same credentials for their Substack account and their ChatGPT account is at risk of having both compromised through a single exposure.
What China’s Espionage Groups Are Doing
Hultquist’s warning wasn’t limited to financially motivated criminal groups. He noted that Google researchers have observed an active Chinese cyber espionage group using the same LLM-jacking techniques to access AI computing infrastructure.
The distinction matters. A criminal group stealing AI credentials to resell cheap access is an economic problem. A Chinese APT using the same methods to access AI compute and training data is a national security problem, one with implications for AI capability development that run directly parallel to the Chinese AI lab distillation attacks against Anthropic we reported on in September.
Those attacks involved seven China-based labs generating 190 million unauthorized Claude exchanges through fake accounts and dark web-purchased credentials. LLM-jacking with compromised enterprise cloud servers is a different mechanism toward a similar goal: accessing AI capability at someone else’s expense, either computational or financial.
Hultquist’s economic framing on this is sharp. “They can acquire that computing power at a much lower cost, while we have to pay full price to defend ourselves,” he told the Financial Times. When attackers can access stolen compute or stolen AI credentials for a fraction of market rate, they face fundamentally different economics from the defenders trying to secure those same systems.
The Invisible Threat in Enterprise AI Deployments
One specific warning from Hultquist deserves its own focus because it’s not obvious: companies in the early stages of enterprise AI deployment may misread attacker-driven compute spikes as normal demand from newly installed systems.
When an organization just rolled out an AI assistant to its staff, the engineering team expects compute usage to jump. Suddenly there’s a new class of user queries going through the cloud, new API calls, new infrastructure load. In that context, an attacker who has breached the cloud environment and is running their own AI workloads on it blends into the expected noise of a new deployment. The alert that should say “someone is running $8,000 worth of unauthorized AI inference on your infrastructure” instead looks like “your AI rollout is generating more traffic than anticipated.”
Distinguishing legitimate enterprise AI use from unauthorized AI workloads requires visibility into what queries are being run, not just that compute resources are being used, and most cloud monitoring defaults to billing alerts rather than workload-content analysis.
Anthropic’s Confirmation
This story doesn’t exist in isolation from what Anthropic itself has been tracking. The company’s latest quarterly misuse report, referenced in both the Dataconomy coverage and its own September threat intelligence release, confirmed that threat actors were detected attempting to exploit Claude tools for malicious purposes in more than 24 countries.
That figure includes the distillation attacks from Chinese AI labs we covered in depth. It also includes a broader range of credential theft, API abuse, and LLM-jacking-adjacent activity that GTIG is now documenting as a market rather than a series of individual incidents.
“Every threat actor is using AI,” Hultquist said. The cleaner framing might be: every threat actor now considers AI access worth stealing.
What to Do
For individual users: Treat AI service credentials with the same seriousness as banking credentials. Use unique passwords not shared with other services, enable two-factor authentication on every AI platform that offers it, and check whether your email appears in known breach databases at Have I Been Pwned. If you’ve reused a breached password for an AI account, change it now.
For businesses: Audit cloud billing dashboards for unexpected compute spikes — not just in aggregate but by workload type. New enterprise AI deployments should come with baseline compute profiling so anomalous usage can be distinguished from legitimate adoption. Rotate API keys and service account credentials for AI platforms regularly, and scope them to the minimum necessary permissions.
For a broader checklist on what to do when credentials are already circulating, our guide on responding to dark web data exposure covers the steps that matter.
Frequently Asked Questions
What is LLM-jacking?
A category of attack that targets access to AI models, either by stealing and reselling AI service credentials at deep discounts or by breaching enterprise cloud servers and running AI workloads on the victim’s computing infrastructure.
How much do stolen AI accounts sell for?
Dark web vendors are reportedly selling unauthorized access to services like ChatGPT and Claude at discounts of up to 97% off the legitimate subscription price. Some offer replacement guarantees if accounts are suspended.
Who first documented LLM-jacking?
Sysdig’s threat research team coined the term in April 2024 after observing attackers using stolen AWS credentials to access Amazon’s Bedrock AI service. Google’s GTIG is now describing a mature market rather than early incidents.
Are nation-states involved?
Yes. Hultquist said Google has observed an active Chinese cyber espionage group using the same methods alongside financially motivated criminal groups.
How can businesses detect AI compute abuse?
By monitoring for unexpected compute spikes correlated with specific workload types, not just aggregate billing increases, and by establishing a baseline of legitimate AI usage from known enterprise deployments before comparing against anomalies.