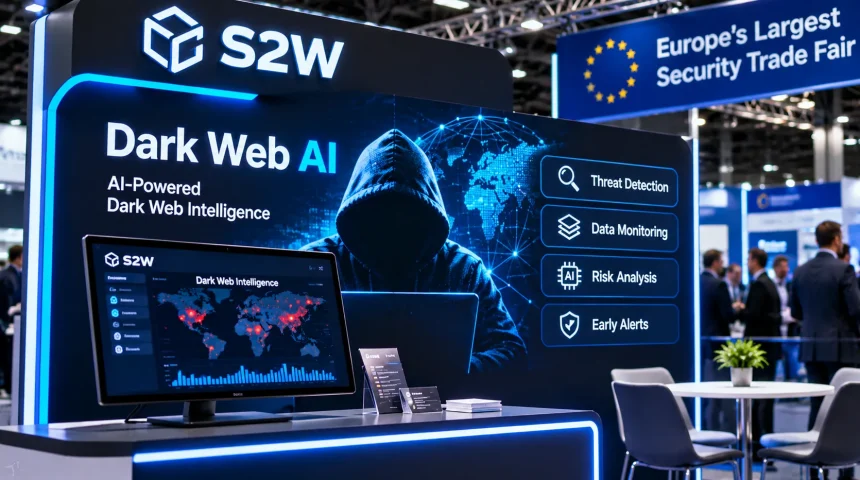
Why S2W Is Focusing on Europe Right Now
S2W CEO Seo Sang-deok said it directly: “Europe is a market of high strategic value, where investment in related technologies and services continues amid tightening cybersecurity regulations.”
That assessment isn’t based on abstract optimism. Europe is in the middle of significant cybersecurity regulatory change. The NIS2 Directive is pushing organizations to treat cybersecurity as a serious compliance matter, not an optional investment. DORA is doing the same for financial services. Both frameworks are driving demand for the external threat intelligence and dark web monitoring that S2W’s products are built around.
S2W also has an existing European reference: last year it supplied Quasar to a Greek government agency. That contract gave the company something harder to claim than booth space at a trade show, a working deployment inside a European public institution. At IT-SA, they used that track record to open conversations with local companies and potential partners.
This move fits a pattern we’ve seen from other Asian security companies in 2026. Fujitsu partnered with KELA to launch a dark web monitoring service aimed at Japanese critical infrastructure, another example of the region exporting specialist dark web intelligence capability into new markets. The difference with S2W is that it’s the intelligence source itself, not just a platform integrating someone else’s data.
What XARVIS Does
XARVIS is S2W’s platform for public institutions, designed for government agencies, law enforcement, and national security organizations that need to track criminal activity across parts of the internet that standard tools can’t reach.
The platform collects and analyses crime-related information from the dark web, Telegram, social networks, and other sources where threat actors tend to communicate. It’s built to help investigators identify specific attackers, build profiles of their activity, and track how they operate over time.
At it-sa, S2W specifically highlighted a new component inside XARVIS called the Deep Research Investigator (DRI). This is an AI agent built specifically for investigation workflows, meaning it doesn’t just return raw search results. It accepts natural-language questions, finds relevant data from across XARVIS’s sources, combines multiple analytical tools, and produces structured results an investigator can act on.
That last part matters. Most dark web intelligence platforms require analysts to formulate technical queries and then manually piece together what they find. DRI shifts that;,an analyst can ask “show me activity linked to this operator on dark web forums and Telegram in the last 30 days” and receive a synthesized output rather than a raw data dump. As we’ve covered in tracking how dark web AI detection is evolving toward multimodal analysis, the shift from raw data retrieval to contextualized AI-driven findings is the defining change in this space right now.
What Quasar Does
Quasar is S2W’s product for the enterprise and institutional side, companies and organizations that need to understand how exposed they are and what attackers are likely to do next.
The platform works by pulling together four things an organization needs to see at once: its externally exposed IT assets, known security vulnerabilities, leaked account credentials that may have surfaced on criminal markets, and attacker activity that’s relevant to their sector or profile.
Most security operations already collect each of those separately. What Quasar does differently is analyze the links between them. It doesn’t just tell you that a credential was leaked; it assesses whether that credential, combined with a known vulnerability in a specific exposed system, means an attack is actively probable. It then ranks recommended responses by urgency.
This is the “before the breach” intelligence that Nasdaq Verafin’s partnership with Q6 Cyber and Ontinue’s ION Dark Web Monitoring are also chasing, turning external threat data into prioritized action rather than a list of alerts. S2W’s differentiation is the depth of its dark web data collection, which traces back to DarkBERT, the model it built with KAIST by training on over six million dark web pages. That training pipeline gives S2W’s intelligence layer contextual understanding of criminal community language and patterns that generic threat feeds can’t replicate.
S2W and the Broader Korean Push Into Dark Web AI
S2W’s appearance at it-sa doesn’t sit in isolation. Earlier this year, South Korea’s government selected a 33-organization consortium , including S2W, to build a 700 billion parameter security AI specifically trained on dark web data. That project, led by Naver Cloud, is designed for deployment at Korean critical infrastructure, including nuclear power and aerospace. S2W contributes the dark web intelligence data layer.
The European push and the domestic national project are running in parallel. S2W is simultaneously contributing intelligence data to a state-level AI security model at home and pitching the commercial versions of those capabilities, XARVIS and Quasar, to European public and private buyers abroad.
The dark web intelligence market is growing at over 21% annually and is projected to cross $2 billion by 2030. A significant share of that growth is happening in Europe, where regulatory drivers are converting what was previously a discretionary security investment into a compliance requirement. S2W is positioning to be a specialist supplier into that expanding market, with a Greek government deployment already on the reference sheet and conversations from it-sa that could extend that track record further.
What Comes Next
S2W didn’t announce a specific new European contract from it-sa; they announced discussions. Whether those discussions convert into formal agreements will play out over the coming months.
The strategic intent is clear. The company wants to turn one European deployment into a pattern of European deployments, using each successive reference to build credibility in a market that’s actively looking for proven suppliers of this capability.
The supply chain attack early warning gap that keeps producing major incidents across Europe , from the Rhysida attack on Berlin’s government to the SilentRansomGroup law firm campaign , is exactly the demand environment S2W is pitching into. The signal that an attack is coming shows up on dark web forums before it arrives at an organization’s door. Platforms that read those signals are no longer a specialist luxury. In 2026’s regulatory and threat environment, they’re becoming expected infrastructure.
Frequently Asked Questions
What is S2W?
S2W is a South Korean data intelligence company specializing in dark web monitoring and cybersecurity AI. It created DarkBERT (in partnership with KAIST) and is listed on KOSDAQ. Its CEO is Seo Sang-deok.
What is XARVIS?
XARVIS is S2W’s cybercrime intelligence platform for public institutions and law enforcement. It collects and analyses crime-related data from the dark web, Telegram, and social networks. The Deep Research Investigator (DRI) is its AI agent that answers natural-language investigative queries.
What is Quasar?
Quasar (also written QUAXAR) is S2W’s cyber threat intelligence platform for enterprises. It analyses externally exposed assets, vulnerabilities, leaked credentials, and attacker activity together to assess attack likelihood and prioritize responses. It was deployed at a Greek government agency in 2025.
What is it- SA Expo & Congress?
Europe’s largest dedicated IT security trade fair, held annually in Nuremberg, Germany. The 2026 edition ran October 27-29 with more than 1,000 companies exhibiting.
Why is S2W expanding into Europe?
Tightening EU cybersecurity regulations (NIS2, DORA) are driving demand for threat intelligence platforms. S2W already has a deployment record in Europe through its Greek government contract.