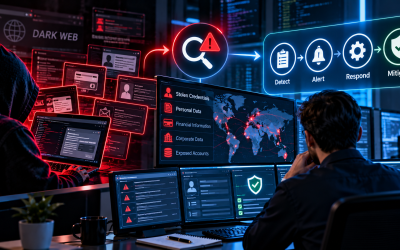
Ontinue launched ION for Dark Web Monitoring (DWM) on October 6, 2026, as a managed add-on to its ION MXDR platform. The service continuously monitors for exposed credentials, typosquatting, and brand impersonation across clear, deep, and dark web sources. Unlike basic monitoring tools that produce raw alerts, Ontinue validates, enriches, and operationalizes findings through its Cyber Defense Center analysts and Microsoft Sentinel integration. IDC data shows roughly one in three MDR customers globally still lack dark web monitoring; the new service targets that gap.
Why Dark Web Monitoring Is No Longer Optional
Ontinue’s CEO Moritz Mann framed the launch clearly. “The security perimeter no longer ends at the edge of the enterprise. Organizations need visibility into the threats that exist beyond their environment, whether that’s stolen credentials being offered for sale, new brand impersonation campaigns, or emerging signs of attacker activity.”
Two statistics from the announcement anchor why that framing is urgent in 2026.
First: exposed credentials can appear on the dark web within 24 hours of a breach. Not weeks. Not days. Hours.
Second: only 19% of organizations currently monitor for credential exposure continuously and automatically remediate it. The other 81% are waiting to find out, usually by being breached.
The gap between those two facts is where attackers live. Credentials from a breached system circulate in criminal markets within hours. The average organization that doesn’t monitor for this typically learns about exposure only after an attacker has already used the credential.
This pattern has shown up repeatedly in our breach coverage through 2026. The Substack breach followed exactly this trajectory: 663,000 user credentials appeared on BreachForums well before Substack’s own systems flagged the incident. The Australian Medicare listing surfaced in a criminal forum on September 28, discovered by a cybersecurity firm conducting routine dark web monitoring, not by the government agency whose data was involved. In both cases, dark web monitoring was the first way any defender learned something was wrong.
The Three Things ION for DWM Actually Monitors
Ontinue’s service covers three distinct threat categories, each addressing a different way organizations are exposed outside their perimeter.
Exposed credentials are the most immediate threat. When a third-party service your employees use gets breached, and in 2026, this happens constantly, the email-and-password combination that an employee used to sign up can end up in a criminal marketplace within hours. If that credential is reused for corporate systems, the attacker now has a valid login. ION for DWM monitors customer-owned email domains across breach databases and criminal marketplaces, alerting when credentials associated with those domains appear.
Typosquatting and brand impersonation are slower-burn but often larger-scale risks. Attackers register domains that look similar to legitimate company names, small character substitutions, added hyphens, different TLDs, and use them to run phishing campaigns or payment fraud. By the time customers or employees realize they’ve been redirected to a fake site, the credential harvest or payment redirection has already happened. ION for DWM continuously detects suspicious domains designed to mimic customer brands and assesses their risk before they’re used in active campaigns.
Emerging external threats is the broadest category, monitoring for early signs that a company is being discussed in criminal communities, that data is being staged before a leak announcement, or that ransomware groups are signaling intent to target specific organizations. Yogesh Shivhare, Senior Research Manager at IDC, described why this category specifically matters: “Credential exposure, ransomware leak staging, and brand impersonation activity on dark web forums often precede or accompany active intrusions.”
What “Managed” Means Here – and Why It Matters
The distinction between a monitoring tool and a managed monitoring service is central to what Ontinue is pitching, and it’s a legitimate distinction worth understanding.
A monitoring tool gives you a stream of alerts. You still need people with the expertise to investigate each finding, determine whether it’s relevant to your specific environment, prioritize it against everything else in your security queue, and decide what action to take. For most mid-market organizations, that means a list of findings nobody has time to work through properly.
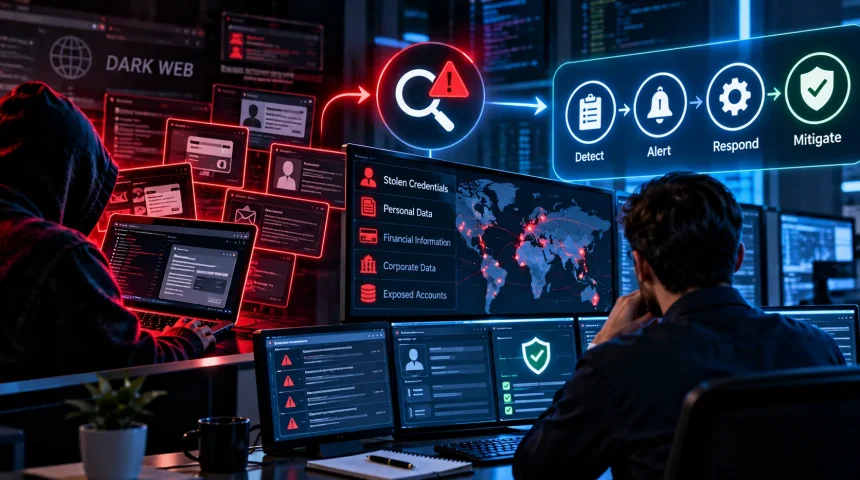
ION for DWM routes every finding through Ontinue’s Cyber Defense Center analysts, the same team already running 24/7 managed security operations for ION MXDR customers. Analysts validate the finding, assess its relevance to that specific customer’s environment, and operationalize it through established ION MXDR response workflows. Approved response actions can be automated or executed with customer oversight based on pre-agreed rules of engagement.
The practical result: dark web findings become treated incidents with actual next steps, rather than another category of noise for an already-stretched security team to sort through. Jason Burzenski, VP of Global Cyber Security at Epiq, one of Ontinue’s customers, summed up the appeal directly: “ION for Dark Web Monitoring expands our visibility beyond our existing tools, giving us better insight into external risks and bringing validated findings into the managed security operations we already trust.”
IDC’s Shivhare noted that providers who “integrate dark web monitoring with analyst-triaged intelligence and actionable takedown capability, rather than delivering raw feed data, are closing that gap in a way that directly improves security outcomes.”
The Microsoft Sentinel Integration Angle
ION for DWM is built specifically for Ontinue’s Microsoft-first security operations model. Dark web findings flow directly into Microsoft Sentinel, the cloud-native SIEM and SOAR platform that sits at the heart of ION MXDR.
This is a meaningful architectural detail for security teams that have standardized on Microsoft’s security stack. External threat intelligence from the dark web appears in the same dashboard. Teams investigate it using the same detection and response workflows as internal security signals, endpoint alerts, identity events, and cloud activity logs. The analyst doesn’t need to context-switch between a dedicated dark web portal and the enterprise SIEM. Everything lands in one place.
For organizations running Microsoft Defender XDR, Azure, and Microsoft 365 as their core security environment, this integration reduces the operational overhead that typically makes dark web monitoring feel like an add-on rather than a core capability.
A Market-Level View of Where This Sits
Ontinue’s launch fits squarely into a trend that the dark web intelligence market data confirms is accelerating: organizations are moving from standalone dark web monitoring tools toward integrated, managed services that combine monitoring with investigation and response. The market is growing at over 21% annually, driven by the exact problem Ontinue is addressing: intelligence without action is noise.
The approach parallels what we’ve seen across the dark web intelligence space this year. Nasdaq Verafin’s partnership with Q6 Cyber delivered banking-specific dark web credential intelligence integrated directly into fraud investigation workflows. Fujitsu and KELA’s collaboration combined dark web monitoring with threat hunting and attack surface management for Japanese critical infrastructure operators. The common thread: dark web signals are only useful when they trigger an action.
IDC’s data point on the scale of the gap is worth repeating. Roughly one in three MDR customers globally still don’t include dark web monitoring in their service. Given what we know about how credential theft fuels the broader fraud and ransomware supply chain, that represents a significant portion of the enterprise security market operating without visibility into one of 2026’s most active threat vectors.
Frequently Asked Questions
What is Ontinue?
A managed detection and response (MDR) provider that operates the ION MXDR platform, which includes a 24/7 Cyber Defense Center staffed by security analysts and an AI-enhanced Agentic SOC.
What is ION for Dark Web Monitoring?
A managed add-on service launched October 6, 2026, that extends ION MXDR to continuously monitor for exposed credentials, typosquatting, and brand impersonation across clear, deep, and dark web sources.
How is this different from standalone dark web monitoring tools?
Rather than generating raw alerts, ION for DWM validates findings, assesses their severity and relevance, and operationalizes them through Ontinue’s analyst team and automated response workflows, integrating directly into Microsoft Sentinel.
Who is this service aimed at?
Organizations running Microsoft-centric security operations that want external threat visibility managed alongside their existing MXDR service, without adding another platform to monitor.
What does the IDC data say about the market gap?
Roughly one in three MDR customers globally currently lack dark web monitoring as part of their service, according to IDC.